Alset for Business
AI training built for your industry.
Hands-on AI courses for every role, built on your teams' real workflows — not generic theory. They build real projects, they actually finish, and you can prove they learned.
How it works
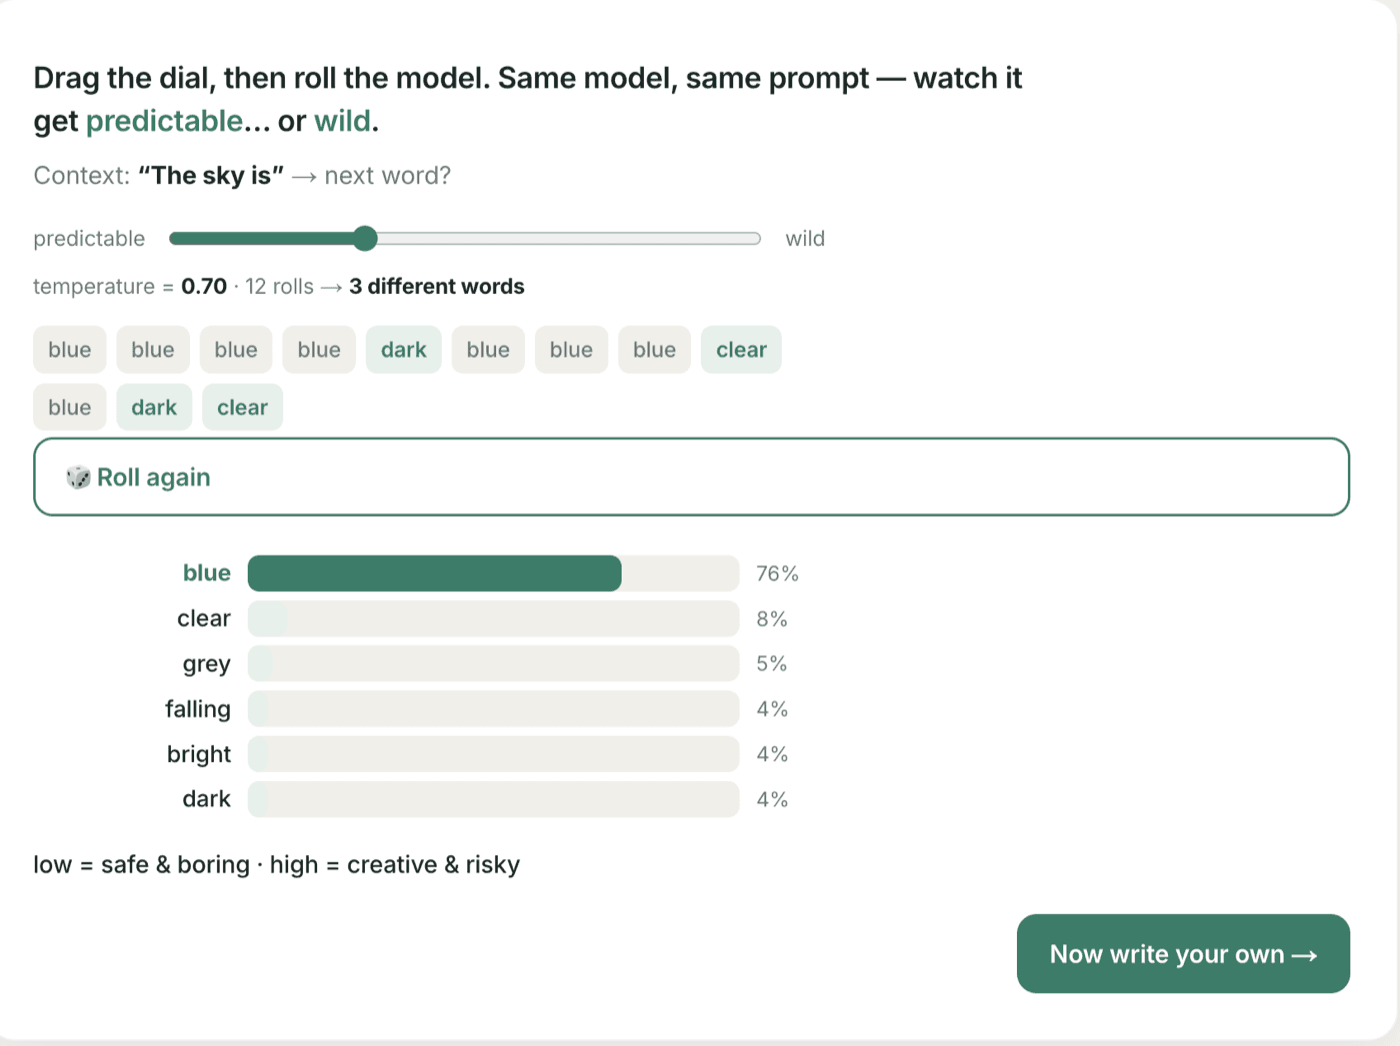
Show mode — built by doing
Watch it work, steer it, then build the real thing yourself — no lecture.
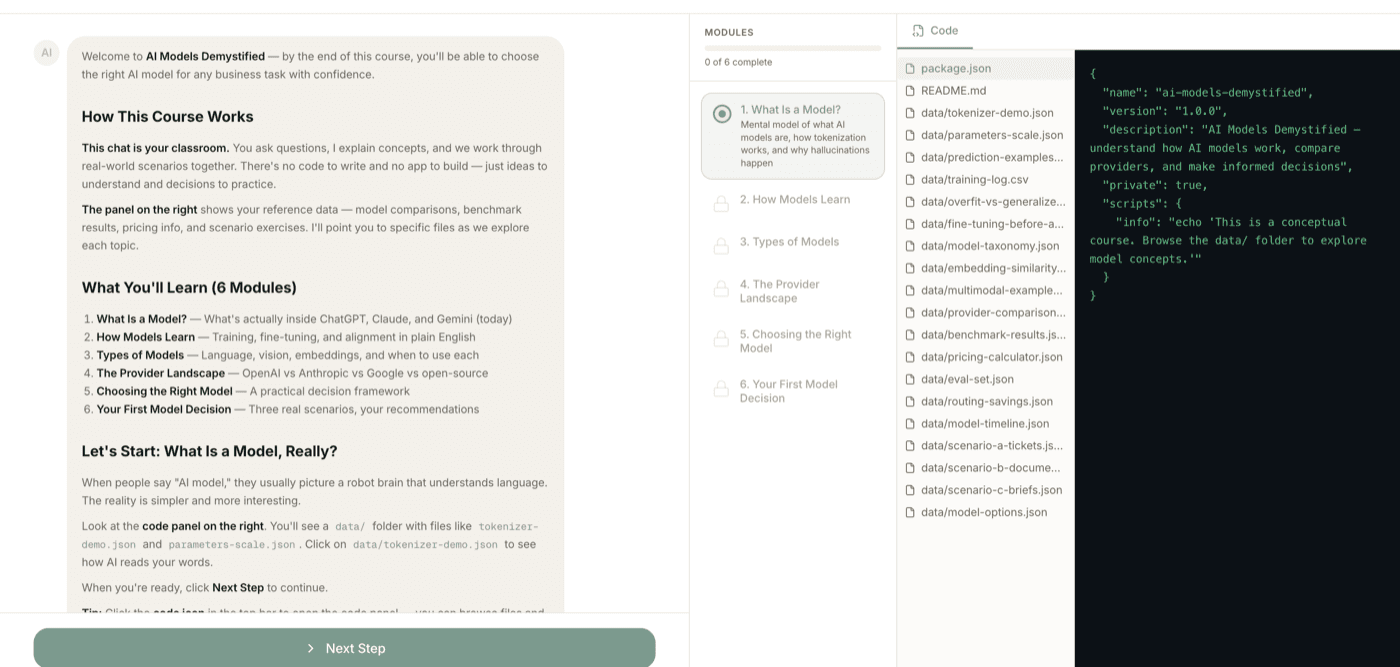
Classic mode — depth on tap
Go as deep as you want, with an AI tutor guiding every step.
Security, Compliance & SRE
Train and prove your team on the frameworks buyers and regulators ask about — the shared core once, then the deep-dives you need — plus the engineering practices that ship safely. Start with the compliance hub, add the spokes and courses that apply.
Compliance Frameworks Decoded
Cut through the alphabet soup. Learn which frameworks actually apply to you (HIPAA, PCI DSS, GDPR, SOC 2, ISO 27001, NIST/CMMC), the ~65% of controls they all share, how to satisfy many at once with one control set, and how to build a compliance roadmap. The hub course — take the deep-dive spoke for each framework you pick. For founders, managers, compliance leads, and engineers.
SOC 2 Readiness
Run your own SOC 2 readiness and walk into the audit prepared. Understand what SOC 2 really is, scope it, implement the common controls, collect evidence that holds across the window, close your gaps, and pass the audit — then keep it. For founders, security/compliance leads, and engineers at B2B software companies.
HIPAA Compliance
Go deep on HIPAA: what the law actually requires, what counts as protected health information (PHI) and who's in scope, the administrative/physical/technical safeguards, the risk analysis OCR looks for, breach notification, and how to run it as a continuous program. The healthcare deep-dive spoke — take it after the Compliance Frameworks hub. Educational, not legal advice.
PCI DSS Compliance
Go deep on PCI DSS: what the card-brand standard actually requires, how to shrink your cardholder data environment (the biggest cost lever), the 12 requirements, how you validate (SAQ, ASV scans, ROC), running a gap assessment, and staying compliant continuously. The payments deep-dive spoke — take it after the Compliance Frameworks hub. Educational, not legal/QSA advice.
GDPR Compliance
Go deep on GDPR: what the EU regulation requires, what counts as personal data and whether you're a controller or processor, lawful basis and data-subject rights, your core obligations (RoPA, DPIAs, DPAs, DPO), breach notification and accountability, and international transfers. The data-privacy deep-dive spoke — take it after the Compliance Frameworks hub. Educational, not legal advice.
ISO 27001
Go deep on ISO 27001 — the international certification European and cross-border buyers ask for. Understand the ISMS at its core, scope it, run the risk assessment and Statement of Applicability, apply the Annex A controls, build the evidence and internal-audit discipline, and navigate certification. The information-security-management deep-dive spoke — take it after the Compliance Frameworks hub. Educational, not legal advice.
Security Awareness (AI-Era)
Spot and stop the attacks that actually hit companies — including the new AI-era ones. Phishing and social engineering, passwords and MFA, handling data safely, shadow AI and prompt injection, and how to report fast when something goes wrong. For every employee, technical or not. Annual + onboarding.
CI/CD Best Practices
Ship faster with fewer incidents. Learn why CI/CD wins, the anatomy of a pipeline, the testing gates that make it trustworthy, deployment strategies (blue-green, canary, rolling), securing the pipeline (DevSecOps), and observability with fast rollback. For engineers, DevOps, and SRE.
Shift-Left Security Scanning
Prevent security problems at the commit, not in prod. The scanner toolchain for shift-left DevSecOps: secrets (Gitleaks), infrastructure-as-code (Checkov), code / SAST (Semgrep), and vulnerabilities (Nuclei & dependency scanning) — plus the fidelity discipline (tuning, triage, gating) that makes the signal trustworthy. For engineers, DevOps, and security. The deep companion to CI/CD Best Practices.
Sensible Security: Defending Against Agentic AI & External Threats
Defend against agentic AI and external attackers with controls that are proportionate to the risk — not fear-driven over-lockdown that strangles the business. Match the control to the risk, shrink your attack surface (including AI), get identity right for humans and agents, govern (don't ban) AI agents, defend against AI-accelerated and autonomous attackers, and design for resilience with fast detection. For security leads, SREs, and technical leaders.
Threat Tradecraft: Detecting Today's TTPs
Threat-informed defense for practitioners: learn today's attacker tactics, techniques, and procedures — mapped to MITRE ATT&CK — and turn each one into a detection. Cover identity & cloud intrusions, AI-era tradecraft, endpoint living-off-the-land & EDR evasion, lateral movement & C2, and ransomware/extortion. Build a reusable TTP detection playbook. For SOC analysts, threat hunters, and detection engineers. Defensive throughout.
Red, Blue & Purple: Ethical Hacking for Your Organization
Understand ethical hacking, red teaming, blue teaming, and purple teaming — and how to make them pay off for your organization. What security testing is (and why authorization is everything), what the hacker tool categories reveal, how red teams emulate real adversaries to test your detection and response, what blue teams do, why purple teaming compounds the value, and how to commission, govern, and act on it all. Build a Red/Blue/Purple program plan. For security and business leaders. Defensive and conceptual throughout.
Security Leadership in the AI Era: Building & Running the Program
Run a modern security program that leverages AI to do more with less — without the hype. For CISOs, security managers, and IT directors: the business of security (strategy, board, budget, team) reframed for the AI era, with the emphasis on how to actually use AI to run security better — the AI-augmented SOC, agentic SecOps with guardrails, and AI across detection, triage, threat intel, IR, and compliance — plus governing AI so you can leverage it safely, and the metrics that prove it works. Build an AI-era security program strategy. Defensive and vendor-neutral; honest about where AI helps and where it doesn't.
AI Governance & AI Security
Govern and secure the AI your organization uses and builds. For governance, risk, and compliance leads: why AI needs its own governance, the frameworks and regulations you now own (NIST AI RMF, ISO/IEC 42001, EU AI Act), how to build the program (AI inventory, risk classification, policies, roles), the AI security risks you must govern (OWASP LLM, agents/RAG/MCP, the AI supply chain) and the controls and assurance to require, and how to run it (monitoring, incident response, audit). Build a complete AI governance & security (AI TRiSM) program. Defensive and vendor-neutral; educational, not legal advice.
Industry & Engineering
Manufacturing
6 role paths · 5 use-cases
Aerospace & Defense
5 role paths · 5 use-cases
Metallurgy & Materials
5 role paths · 5 use-cases
Mining & Minerals
5 role paths · 5 use-cases
Energy & Utilities
5 role paths · 5 use-cases
Civil & Infrastructure
5 role paths · 5 use-cases
Automotive & EV
5 role paths · 5 use-cases
Food Processing & Agri
5 role paths · 5 use-cases
Engineering (General)
5 role paths · 5 use-cases